

The same access and quality controls matter when evaluating healthcare revenue cycle outsourcing for claims, billing, and account follow-up work.
A signed BAA does not prove that every patient call is secure. The real test is whether an outsourcing partner can show how its controls work when agents handle PHI.
Need help reviewing a healthcare support partner? Schedule a consultation with Arvios to discuss the call center scope, PHI touchpoints, and operational safeguards your team should confirm before outsourcing.
HIPAA compliant call center outsourcing requires documented proof that PHI is protected during calls, follow-ups, recordings, QA reviews, and system updates. Buyers should verify safeguards, role-based access, training, incident response, subcontractor controls, and a business associate agreement before granting access.
The question is not whether a vendor says it is compliant, but whether your team can verify the safeguards behind that claim. The next section, HIPAA compliant call center outsourcing starts with the right questions, shows how to begin that review. Here’s how.
HIPAA compliant call center outsourcing starts with the right questions
A strong first review asks what PHI the vendor needs, who can access it, how access is limited, and how exceptions are reported. Arvios recommends treating broad compliance claims as prompts for evidence, not as final answers.
Healthcare leaders searching for HIPAA compliant call center outsourcing are not just comparing prices. They are deciding whether a vendor can handle patient conversations without adding avoidable risk. Start with a checklist before sharing PHI, sample records, or system access. This keeps the first review focused on proof, not broad claims.
The buyer’s first filter
A call center may become a business associate when it handles PHI for a covered entity. The U.S. Department of Health and Human Services says covered entities need satisfactory assurances that business associates will safeguard PHI. They must also use it only for the work they were hired to do.
Ask what data the vendor needs for each workflow. Appointment scheduling may expose different details than billing support or care coordination. Then map each workflow to access levels, call recordings, messaging tools, and quality reviews. A review of medical call center compliance standards can help frame the operational questions.
Business associate expectations
A business associate agreement is not the end of the review. It is the starting point for clear duties. Ask who can access PHI, where access occurs, and how permissions are granted or removed. Request written answers for training, monitoring, breach response, and the minimum necessary use of PHI.
Also ask whether subcontractors can create, receive, maintain, or transmit PHI. HHS explains that business associates must enter into business associate agreements with subcontractors that handle PHI on their behalf. Your checklist should request the subcontractor review process and the path for addressing a violation.
Evidence to request before PHI access
Do not treat a general compliance statement as a complete answer. Ask the vendor to show how its controls work in the planned call center workflow. The review should cover people, systems, and facilities. It should also name the owner for each control and the evidence available for review.
- Which roles can view PHI, and how is access limited by workflow?
- How are agents trained before access is granted, and how is training tracked?
- How are calls, recordings, and screen activity monitored?
- What happens when an agent changes roles or leaves the team?
- How does the vendor report a suspected incident to your organization?
- Which subcontractors may touch PHI, and how are they reviewed?
For Arvios buyers and healthcare operations teams, this checklist helps operations, compliance, and security teams ask the same questions. It also gives procurement a clear record before implementation planning begins.
What should a HIPAA-ready call center prove before kickoff?
Before kickoff, a HIPAA-ready call center should provide a reviewable package of contracts, safeguards, training records, access maps, incident response steps, and subcontractor controls. The goal is to confirm how protections work before agents touch PHI.
Before kickoff, ask for evidence, not a broad promise of compliance. HIPAA compliant call center outsourcing starts with a reviewable package of contracts, controls, records, and named owners. This package should show how the partner protects PHI during daily work.
A call center that handles PHI for a covered entity may act as a business associate. HHS says covered entities need satisfactory assurances from business associates that PHI will be safeguarded and used only for the work requested. A signed BAA is the starting point, not the full review.
Contract and safeguard evidence
Ask for a draft BAA early. Then request documented policies for administrative, physical, and technical controls. The HIPAA Security Rule safeguards give buyers a clear frame for the review. The partner should also show its risk review process and the owner for each control.
Review the access map at the workflow level. Agents should receive only the systems and PHI needed for assigned tasks. Ask how managers approve access, remove access after role changes, and review audit trails. The answers should be specific enough to test before launch.
| Review area. | Proof-ready partner. | Weak response. |
|---|---|---|
| BAA readiness. | Shares a draft and named owner. | Promises paperwork after launch. |
| Safeguards. | Maps written controls to workflows. | Uses a generic security statement. |
| Access. | Shows roles, approvals, and removal steps. | Grants broad team access. |
| Workforce. | Provides training records and refresh plans. | Says agents are trained. |
| Incidents. | Names escalation owners and reporting steps. | Has no clear handoff path. |
| Subcontractors. | Lists vendors and downstream BAA controls. | Cannot explain vendor oversight. |
Workforce and incident proof
Request training records for the assigned workforce, including refresh plans and completion tracking. Ask for sample audit reports or redacted access logs. These items show whether controls reach the agent desktop instead of staying in a policy folder.
Ask the partner to walk through a breach escalation example. The path should cover detection, internal review, client notice, documentation, and corrective action. If service runs after hours, apply the same review to 24/7 HIPAA-compliant healthcare support.
Controls that continue after launch
The evidence package should name every subcontractor that may create, receive, maintain, or transmit PHI. It should also show downstream BAA controls and the response process for a vendor issue. Finally, ask how scripts, screens, recordings, and reports limit PHI to the minimum needed for each task.
Set a recurring review cadence before kickoff. Review access changes, training gaps, audit findings, incidents, and subcontractor changes with named owners. This turns the checklist into an operating control rather than a one-time sales exercise.
How to evaluate PHI handling and access controls
Evaluate PHI handling by tracing a patient interaction from intake to notes, recordings, reports, QA review, and retention. Then confirm unique user accounts, role-based permissions, MFA where appropriate, audit logging, and fast access removal after role changes.
Trace PHI through the workflow
Start with a live walkthrough, not a broad promise of compliance. Ask the provider to map where PHI enters, which systems hold ePHI, and where agents can view it. The review should cover calls, notes, tickets, recordings, exports, and quality checks. This is a core part of evaluating medical call center compliance standards.
Next, ask whether call recording is on for every queue or limited by use case. Confirm where recordings are stored, who can play them, and how the provider handles downloads. Ask how recordings are retained and removed. If agents use more than one platform, trace PHI across each handoff instead of reviewing the phone system alone.
Access controls at the agent level
HIPAA compliant call center outsourcing requires more than a secure facility. The HHS Security Rule calls for administrative, physical, and technical safeguards. Use the Security Rule requirements as a baseline for vendor questions. Ask the provider to show how users sign in, gain access, change roles, and lose access after departure.
Request a role matrix for agents, supervisors, trainers, quality staff, and IT admins. Check whether each role can access only the systems and records needed for its work. HHS states that business associates must make reasonable efforts to limit PHI to the minimum necessary for the purpose. That minimum necessary standard should be visible in daily operations.
- Ask whether each agent has a unique account and whether shared logins are blocked.
- Confirm whether multi-factor authentication applies to systems that hold or display ePHI.
- Review how access is approved, changed, logged, and removed.
- Confirm how the team limits screen views, exports, downloads, and local storage.
- Inspect workstation rules for unattended screens, paper notes, and personal devices.
Offshore governance in practice
For an offshore team like the healthcare support models Arvios helps organizations evaluate, ask how site controls are enforced during each shift. Review secure workstation rules, clean desk checks, visitor controls, floor access, and supervisor oversight. Then ask for proof that managers test those controls in practice. Written policies matter, but buyers also need to see how the site applies them.
Map every subcontractor that may create, receive, maintain, or transmit PHI. Confirm whether the right business associate agreement covers each party. Ask which party reviews access and how issues are raised. The provider should explain its response path for suspected access incidents. A clear review should name the owner, the first response steps, and the records available for audit.
Training, QA monitoring, and escalation questions to ask
Training, QA, and escalation should be healthcare-specific, documented, and recurring. Ask how agents learn PHI rules, how supervisors score privacy steps, how coaching is recorded, and how a possible privacy incident reaches your team.
HIPAA compliant call center outsourcing requires more than an onboarding presentation. Ask how the provider trains each agent who may handle protected health information (PHI). HHS states that HIPAA compliance training is mandatory for employees who handle PHI. The provider should explain how it checks understanding before an agent starts work.
Healthcare-specific training
Training should match the work your team will assign. Ask whether agents practice patient identity checks, minimum-necessary access, secure message handling, and safe call transfers. For context, review the role of medical call center compliance standards when you define the scope. Generic customer service training is not enough for healthcare workflows.
Also ask what triggers a refresher. A sound answer should cover new workflows, policy updates, audit findings, and coaching after errors. Request sample training records and completion logs. Ask how the provider removes access when an agent has not passed a required check.
Quality monitoring and coaching
Quality assurance (QA) should continue after launch. Ask how the provider samples interactions, scores them, and records coaching. The review should separate service quality from privacy controls. A polite call can still create risk if an agent skips an identity check or shares more PHI than needed.
Use specific questions during vendor review:
- Which call, chat, or email interactions enter QA review?
- Which privacy steps appear on the scorecard?
- Who reviews failed interactions, and how is coaching recorded?
- How do recurring errors change training or access?
- Which reports will your operations and compliance teams receive?
Ask to see a redacted scorecard and a sample coaching log. This shows whether the provider can document its process, not just describe it. It also helps your team confirm that QA covers the channels in scope.
Complaint and incident escalation
Escalation paths need the same level of detail. Ask agents to tell a service complaint from a possible privacy incident. Then confirm who receives each issue, what must be documented, and how your team is notified. Business associates must provide breach notification to the covered entity when unsecured PHI is breached.
Request an escalation map with named roles, backup contacts, handoff steps, and recordkeeping rules. Ask how the provider tests that process and updates it after a review. Compliance should remain part of daily operations, QA meetings, and coaching. It should not sit in a file after onboarding ends.
Steps for comparing healthcare outsourcing vendors
Compare vendors with one scorecard that weighs scope fit, service quality, compliance evidence, cost, references, and pilot results. Arvios works best with healthcare buyers who want a dedicated support model instead of a generic outsourced queue.
Start with a written scope, not a vendor presentation. For HIPAA compliant call center outsourcing, compliance is the baseline for comparison. If a vendor handles protected health information (PHI), ask for evidence that matches the work. HHS states that covered providers and health plans need satisfactory assurances from business associates. PHI may be used only for the stated purpose.
Intake scope and risk boundaries
Map the call types, systems, hours, languages, and expected volume before requesting proposals. Note which tasks require PHI access and which can use limited data. This keeps cost estimates tied to the same workload. It also shows where a vendor must prove safeguards, training, and clear ownership.
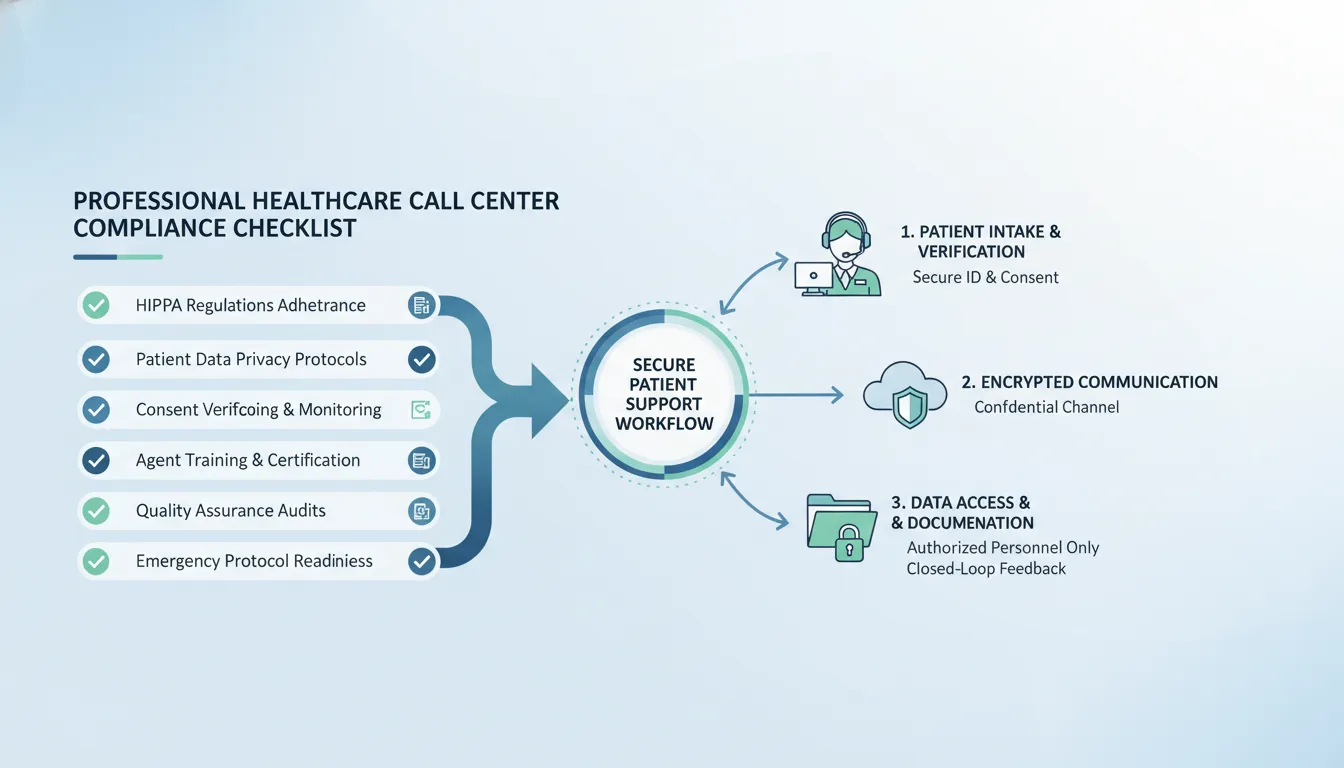
A scored vendor review
Use one scorecard for each vendor. Weight cost, service quality, and compliance risk based on your operation. A low price has little value if the staffing plan creates delays or weak controls. Ask each vendor to support answers with documents, workflow examples, and named owners.
- Define the intake scope. List call reasons, service hours, systems, escalation paths, and PHI touchpoints. Separate required services from options.
- Review the BAA and subcontractor chain. Confirm who may create, receive, maintain, or transmit PHI. Ask how the vendor manages each subcontractor.
- Test operational safeguards. Review access controls, agent training, physical security, audit routines, and incident response. Ask for proof, not broad statements.
- Compare cost with service design. Check pricing assumptions, staffing ratios, coverage windows, and ramp plans. Model the likely savings against transition effort and oversight needs.
- Run reference checks. Speak with healthcare clients that use a similar scope. Ask about launch issues, quality trends, staff turnover, and response during incidents.
- Set a limited pilot. Track answer speed, abandonment, resolution, quality review scores, escalation rates, and compliance findings. Define pass thresholds before the pilot starts.
Pilot evidence and final selection
A pilot should test the proposed operating model under a controlled scope. Compare quality and risk findings with the quoted cost. If the service includes continuous coverage, review the staffing assumptions behind 24/7 HIPAA-compliant healthcare support. Require a written plan for any gap found during testing.
Arvios encourages buyers to keep the risk review active after selection. HHS describes risk assessment as central to Security Rule compliance. Set review dates, owners, and escalation rules in the operating plan. That gives operations leaders a repeatable way to monitor cost, quality, and risk after launch.
Red flags that a vendor is not ready for regulated healthcare work
Red flags include vague compliance statements, reluctance to discuss a BAA, weak audit trails, and no healthcare QA process. Unclear subcontractor oversight or poor incident reporting should also pause the buying process until the vendor provides proof.
HIPAA compliant call center outsourcing requires more than a broad claim on a sales page. A vendor should explain how its team handles protected health information (PHI) during routine calls and unusual events. Buyers should treat vague answers as a reason to pause.
Vague compliance answers
Ask a vendor to describe its safeguards, staff training, access controls, and incident response process. The HIPAA Security Rule calls for administrative, physical, and technical safeguards. A vendor that only says it is “HIPAA compliant” has not shown how those safeguards work in practice.
Resistance to a business associate agreement (BAA) is another serious warning sign. The vendor should be ready to discuss its duties, reporting path, and contract terms with your legal team. A rushed or evasive answer creates risk before service even begins.
Missing proof and weak reporting
Policies need to be visible in the operating model. Ask for written workflows for identity checks, call handling, escalation, quality review, and suspected incidents. Compare the answers with the practical expectations behind medical call center compliance standards.
Weak audit trail reporting is also a concern. A vendor should explain what it logs, who reviews the logs, and how it can investigate an event. Generic agents with no healthcare QA process may miss the context needed for safe patient support.
- No sample workflow for calls involving PHI.
- No clear owner for compliance questions.
- No reporting process for suspected unauthorized access.
- No healthcare-specific QA checks or coaching path.
- No useful description of agent access limits.
Unclear subcontractor oversight
Ask which subcontractors can create, receive, maintain, or transmit PHI. Also ask how the vendor checks their work and responds to problems. HHS states that business associates must enter BAAs with subcontractors that handle PHI on their behalf.
A vendor should not hide this part of its delivery chain. The HHS business associate fact sheet also notes direct liability for key HIPAA duties. If the vendor cannot map access, agreements, and escalation steps, it is not ready for regulated healthcare work.
What does a safer transition plan look like?
A safer transition plan limits PHI access until the team, systems, scripts, escalation paths, and reporting cadence are tested. Start with a controlled pilot, assign owners, review findings, and expand only after gaps are corrected.
A safer launch is controlled, documented, and easy to pause. For HIPAA compliant call center outsourcing, start with a narrow scope instead of moving every workflow at once. Define the call types, systems, user roles, hours, and escalation paths included in the first phase.
Scope and PHI exposure
Map where protected health information enters the workflow, where it is viewed, and where it may be stored or shared. Include call recordings, screen notes, ticket fields, email follow-ups, and quality review tools. The map should show which role can reach each data type.
Use the map to limit access. HHS states that business associates must make reasonable efforts to limit PHI to the minimum necessary for the purpose. Align each agent role with the work it needs to complete, not with broad system access.
- Set the first-phase call queues and approved systems.
- List each PHI touchpoint and the role that needs access.
- Confirm who owns access changes, incident review, and client updates.
- Write standard operating procedures for common calls and exceptions.
Training before go-live
Train the assigned team before live calls begin. Cover identity checks, approved disclosures, note handling, call transfers, and prohibited actions. Add role-based practice with realistic cases. Include a caller who fails verification and an agent who suspects improper access.
Training should match the workflows in the pilot. It should also reflect the administrative, physical, and technical safeguards described in the HHS Security Rule guidance. Document attendance, test results, coaching, and the rule for removing access when an agent is not ready.
Pilot controls and escalation
Start with a limited pilot, then review performance before adding queues or hours. The first review cycle should examine sampled calls, quality scores, access exceptions, escalation timing, and audit logs. Pair the findings with the same medical call center compliance standards used in the wider operating model.
Keep escalation steps simple. Agents need to know when to stop a call, protect the record, alert a supervisor, and document the event. The client and outsourcing partner should review issues together, assign owners, and update the SOP when a gap appears.
The transition plan should include a clear gate for expansion. Add volume only after the team has resolved pilot findings and confirmed that access rules still fit the work. This approach keeps quality review active as the program grows.
Frequently Asked Questions
Does HIPAA prohibit offshoring call center operations?
No. HIPAA does not prohibit offshore call center operations, but location does not reduce the compliance standard. Buyers should confirm how offshore access to PHI is assessed, limited, monitored, and protected. The vendor should also explain its safeguards, workforce controls, and incident process before receiving patient data.
What challenges does HIPAA-compliant call center outsourcing solve?
HIPAA-compliant call center outsourcing can help healthcare organizations scale patient support while keeping PHI handling consistent. A qualified partner can document procedures, control agent access, train staff, and support incident reporting. Outsourcing does not transfer accountability. Buyers still need to vet the vendor and monitor performance after launch.
What should a healthcare organization verify before signing a call center contract?
Verify the vendor’s safeguards, PHI access rules, training records, audit process, incident response plan, and subcontractor controls. Confirm that the contract includes a business associate agreement. The HHS business associate fact sheet explains that business associates can be directly liable for key HIPAA requirements.
How should a buyer evaluate subcontractors used by an outsourced call center?
Ask the call center to identify every subcontractor that may create, receive, maintain, or transmit PHI. Review each subcontractor’s role, access level, safeguards, and incident obligations. According to HHS guidance for business associates, a business associate must enter into agreements with subcontractors that handle PHI on its behalf.
How often should outsourced call center compliance be reviewed?
Review compliance before launch and on a recurring schedule after operations begin. The review should cover training, access rights, audit findings, security controls, incident reporting, and subcontractor changes. Repeat the review when workflows, systems, locations, or PHI access patterns change. The cadence should match the organization’s risk assessment and oversight requirements.
Ready to strengthen your healthcare call center?
Waiting until call volumes strain your team can turn a careful vendor review into a rushed decision. Starting now gives your stakeholders time to define expectations, surface concerns, and choose a path that fits your compliance priorities. An early conversation also makes it easier to plan next steps without adding pressure to your current operations.
Ready to assess your outsourcing options? Schedule a consultation with Arvios to discuss your needs, timeline, and compliance priorities. Bring your current questions so your team can leave with a clearer plan for a careful vendor review. Starting the conversation now helps you move forward with purpose rather than wait for operational pressure to make the decision harder.
